Exposure management platform for network configuration risk
Unify attack surface exposures from routers, switches and firewalls so your team can prioritize remediation, validate segmentation, and reduce cyber risk exposure.

Reduce attack surface exposures created by network configuration
You must prove that segmentation, access, and device hardening hold up under pressure. But many of the most damaging exposures come from network configuration gaps, not missing patches.
CISA and NSA often highlight misconfigurations, like weak segmentation and poor access controls, as common paths to compromise.
Proactive exposure management starts with security control validation: confirming whether network devices enforce the controls your security program depends on.
Nipper OmniSight checks configurations at scale, links findings to exposure risk, and helps your team find and fix attack paths fast.
in 24 hours
Network exposures you can act on
Most unified exposure management programs miss the network control plane. That leaves your team debating risk, chasing noisy findings, and discovering segmentation failures too late. Nipper OmniSight surfaces configuration-driven attack surface exposures and helps you prioritize remediation based on exploitability and impact.
Hidden misconfigurations
Find weak passwords, unsafe services, and insecure admin access on network devices. These gaps are often missed by vulnerability scans and NDR tools.
Segmentation that fails in practice
Confirm whether routing, ACLs, and firewall rules enforce intended trust boundaries and limit lateral movement to sensitive data.
Remediation without clear priorities
Prioritize remediation using exploitability context, attack-path relevance, and business impact so teams focus effort where risk reduction is measurable.
Collect configuration evidence safely
Model devices and test attacker paths
Virtual device modeling runs adversary-style checks to show where weak controls create paths to sensitive data.
Prioritize by exploitability and impact
Map findings to exposure scenarios. This helps teams prioritize fixes that block reachable attack paths. It also drives measurable risk reduction.
Prove fixes with repeat assessment
Re-run assessments whenever you need to. Or run them on a set schedule. Use the results to confirm fixes. Show leaders and auditors how risk is going down over time.
Make network exposure measurable and defensible
Network security work stalls when teams cannot show what can be exploited, where it can be reached, and which fixes matter most. Nipper OmniSight provides configuration-backed evidence so you can prioritize remediation, validate controls, and report outcomes in risk reduction with audit-ready findings.
Configuration-driven exposure discovery
Find configuration weaknesses and potential vulnerabilities across routers, switches, and firewalls using configuration evidence. Surface weak credentials, unsafe management access, risky services, and control-plane weaknesses that expand attack surface exposures. Use the results to harden baselines and reduce repeat findings across the estate.
Segmentation and security control validation
Validate whether segmentation intent is enforced in device settings, not just documented in diagrams. Assess routing, firewall policy, and access controls to confirm least-privilege access and Zero Trust boundaries. When controls are weak or uneven, you get clear proof to align network and security teams on fast, safe fixes.


Risk scoring and prioritized remediation
Prioritize remediation based on exploitability and potential impact, so engineering time goes to the exposures that matter most. Use clear evidence and a defensible risk score to explain priorities to stakeholders. Reports include device-specific guidance to reduce manual effort and speed fixes.
Choose the right tier of Nipper OmniSight for you
Nipper OmniSight is an exposure management platform for the network control plane. Use Nipper OmniSight (Standalone) or Nipper OmniSight (Integrated) for Threat Exposure Management (TEM) through scheduled assessments. Choose Nipper OmniSight (Continuous) when you need continuous threat exposure management (CTEM) for network change.
Bring exposure context to existing workflows
Enrich CMDB, SIEM, and investigation workflows with configuration-validated exposure context. Practitioners get faster triage and clearer fixes. Decision makers get defensible reports on control strength and risk reduction. This does not force network teams to change how they work.
Talk to a network security specialist
Share your exposure management goals and the network environments you need to protect. We’ll map the right Nipper OmniSight tier to your use cases. This covers scheduled assessments and continuous threat exposure management. We’ll also help you define measurable risk reduction for your security program.
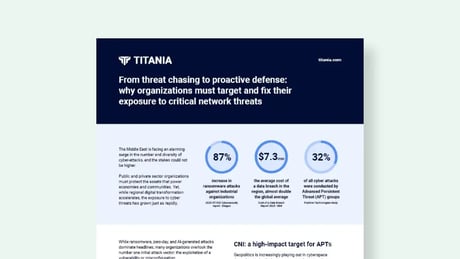
Guides for network exposure management
Frequently asked questions
These answers focus on managing exposure in the network control plane. This is where misconfigurations, weak segmentation, and access policy gaps can create attack paths.
-
An exposure management platform helps you discover and prioritize the exposures most likely to lead to compromise. For network security teams, that means validating network configuration and segmentation controls, not just scanning for CVEs. This helps remediation focus on reachable, high-impact attack surface exposures.
-
Vulnerability scans are essential, but they focus on software flaws. They do not show whether network devices are securely configured, whether access is restricted, or whether segmentation rules are enforced. Nipper OmniSight adds network configuration evidence and control validation so teams can prioritize remediation more accurately.
-
Yes. Nipper OmniSight (Standalone) is designed for scheduled assessments at scale without CMDB dependency. If you have a CMDB or configuration storage platform, Nipper OmniSight (Integrated) can ingest that context. It does this in a read-only way to improve scoping and reporting.
-
Yes. Nipper OmniSight (Continuous) supports continuous threat exposure management by monitoring network configuration change and highlighting exposures created by drift or unsafe updates. If you do not need CTEM-level monitoring, Nipper OmniSight (Standalone) and Nipper OmniSight (Integrated) support scheduled exposure assessments. These assessments are repeatable and support Threat Exposure Management (TEM).
-
Teams can cut the amount of time spent on validating noisy findings. They can also prioritize remediation more confidently, and improve segmentation assurance for critical services. Over time, repeated assessments show risk reduction across digital and internet-facing assets. They support audit evidence and security program reporting.