Skip to Content

Nipper InfraSight trial

Start your Nipper InfraSight configuration security assessment

Assess exported device configurations to find exploitable gaps, prioritize fixes and produce audit-ready evidence – without touching live devices.

Prove what your routers, switches and firewalls enforce

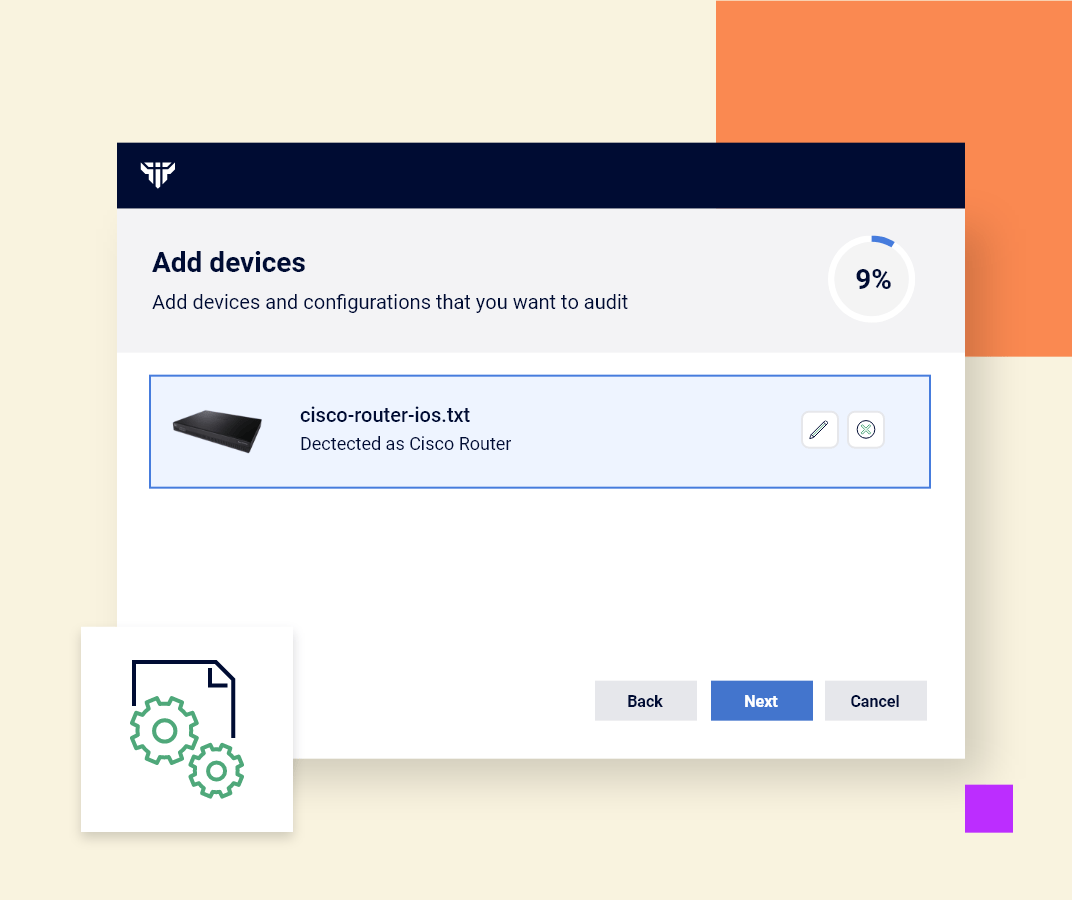
Nipper InfraSight is Titania’s trusted point-in-time configuration assessment solution for network infrastructure. It reviews exported configurations from routers, switches, firewalls, SD-WAN devices and wireless access points (available in the Compliance and Air Gapped tiers of Nipper InfraSight) to identify exploitable misconfigurations, hardening gaps, credential risks, unsafe services and compliance failures.

No agents, no live scanning and no direct device access required. Nipper InfraSight gives network security, audit and GRC teams clear, device-level evidence they can act on, retest and defend.

Start a trial to:

  • Find critical vulnerabilities and misconfigurations in exported configs
  • Validate device hardening against best practice and internal baselines
  • Prioritize remediation by risk and exploitability
  • Generate audit-ready compliance evidence
  • Reduce assessment time without disrupting production networks
Start my assessment

Please fill out the fields below

Trusted by elite security organisations

what-is-nipper-infrasight

What is Nipper InfraSight?

Nipper InfraSight is a configuration-led network security assessment solution and part of Titania’s Nipper solutions family. It assesses exported device configurations offline to identify vulnerabilities, misconfigurations and compliance gaps across the routers, switches, firewalls, SD-WAN devices and wireless infrastructure (available in the Compliance and Air Gapped tiers of Nipper InfraSight) that enforce access and segmentation.

Where scanners and monitoring tools rely on live access, credentials or traffic visibility, Nipper InfraSight works from device configuration insight. It gives teams point-in-time, defensible evidence of what each device permits, where controls are weak and what needs fixing first.

How does Nipper InfraSight work?

Nipper InfraSight imports exported device configurations and builds a device-level model of the settings, rules and controls in place. It then applies security checks, vulnerability intelligence, compliance mappings (available in the Compliance and Air Gapped tiers of Nipper InfraSight) and hardening guidance to surface:

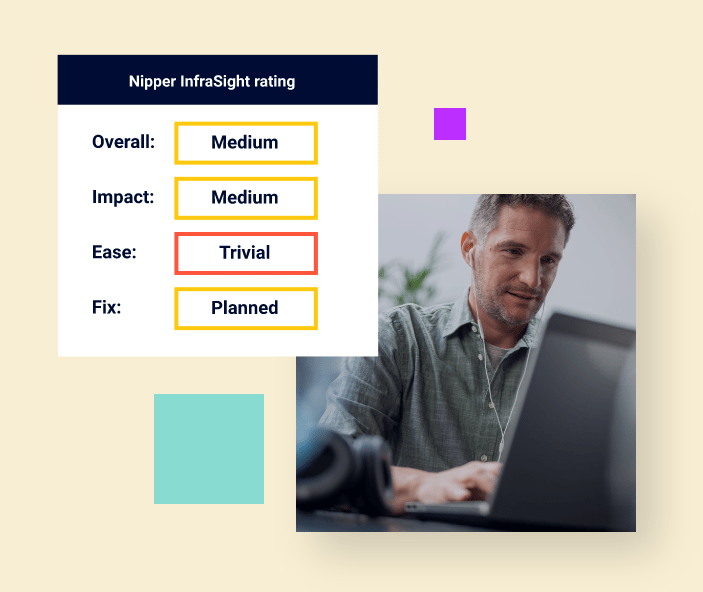
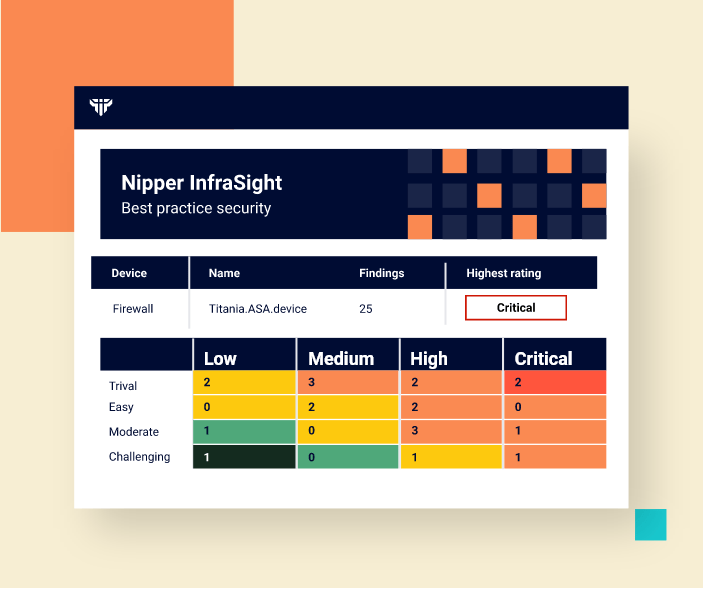
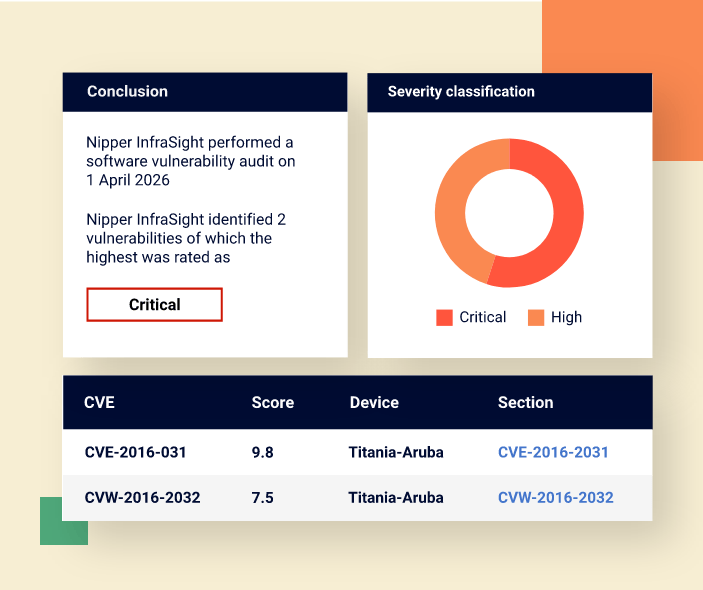
Findings are prioritized so practitioners can focus on the issues most likely to increase exposure or cause audit failure. Because assessments are repeatable, teams can retest after remediation and use the outputs as defensible evidence for stakeholders, auditors and regulators.

Why does configuration exposure matter now?

Routers, switches and firewalls enforce the controls that decide who can access what, how incidents are contained and whether critical systems remain protected. But those controls can drift, conflict or become ineffective as networks change.

Periodic manual reviews cannot keep pace with configuration change, and active scanning is not always permitted in regulated, restricted or air-gapped environments. Nipper InfraSight helps teams reduce device configuration risk using offline, point-in-time evidence that is fast to generate, easy to repeat and suitable for audit reporting.

Which teams use Nipper InfraSight?

Nipper InfraSight is built for teams that need precise, defensible insight into network device configuration risk:

Trial configuration risk assessment

Assess exported configurations to understand where individual devices are creating avoidable risk. During your trial you can:

  • Find configuration weaknesses across routers, switches and firewalls
  • Prioritize vulnerabilities and misconfigurations by risk
  • Use device-specific remediation guidance to reduce time-to-fix
  • Retest after remediation to evidence improvement
configuration-risk-assessment

Trial network device hardening validation

Validate whether device configurations align to internal baselines, best practice guidance and supported benchmarks. Nipper InfraSight helps identify:

  • Weak management-plane settings
  • Unsafe services and protocols
  • Loose firewall or access-control rules
  • Credential, authentication and logging gaps
network-hardening-validation

Trial vulnerability prioritization with configuration context

Move beyond generic vulnerability lists by assessing known weaknesses in the context of your running device configurations and whether they are functioning as intended. Nipper InfraSight helps teams understand:

  • Which vulnerabilities are relevant to the assessed configuration
  • Which issues create the highest practical risk
  • Which devices need urgent remediation
  • Which fixes can be evidenced and reported after retesting
vulnerability-prioritization

Trial compliance evidence automation

Generate repeatable, audit-ready evidence from exported device configurations, mapped to the frameworks and standards you report against. Supports organizations working towards:

  • NIST NVD*
  • PCI DSS**
  • CIS**
  • CMMC**
  • STIGs**
  • NIST SP 800-53**
  • NIST SP 800-171**

* Available in all Nipper InfraSight tiers
** Only available in Compliance and Air Gapped tiers of Nipper InfraSight** Only available in Compliance and Air Gapped tiers of Nipper InfraSight

vulnerability-prioritization

How Nipper InfraSight works alongside scanners and exposure platforms

Nipper InfraSight complements scanners, NDR and exposure platforms by validating the device configuration layer they do not fully prove. It helps teams understand whether routers, switches and firewalls are hardened correctly, whether known vulnerabilities are relevant in context and whether evidence is strong enough for audit.

Whether you are starting with configuration risk assessment, expanding into device hardening and vulnerability prioritization, or need to analyze complex filtering rules and produce audit-ready compliance evidence, the Nipper InfraSight trial helps you explore the capabilities that matter most to your team.

Scanners, NDR and broad exposure platforms Nipper InfraSight
Assess software vulnerabilities and external signals Validates the network configurations that enforce access and containment
Require connectivity, credentials or agents on live systems Works from extracted or minimally collected configurations – no agents, no cloud, no live scanning
Infer whether controls are working Proves whether controls are working, with preserved evidence
Often generate high finding volumes with limited context Ranks findings by exploitability and impact, with device-specific remediation
Constrained in restricted and air-gapped environments Designed for regulated, high-consequence and air-gapped environments
Limited visibility into segmentation enforcement Validates segmentation boundaries and least-privilege access

What happens after I register?

Trusted where failure is not an option

1000+ organizations trust Nipper
100+ critical infrastructure providers
169 government and defense organizations
30+ US federal agencies
180+ device types
20+ vendors
43 Operating in 43 countries across 6 continents
80% reduction in audit prep time

Frequently asked questions